In an increasingly data-driven world, understanding and adhering to data privacy regulations is paramount for any online platform. For phpFox community owners, the General Data Protection Regulation (GDPR) isn’t just a buzzword; it’s a critical framework that impacts how you manage user data and build trust within your community. Ignoring GDPR can lead to significant penalties, but more importantly, it can erode the very foundation of trust your community is built upon.
What is GDPR and Why Does it Matter to You?
GDPR is a comprehensive data protection law enacted by the European Union. While it originated in the EU, its reach extends globally, affecting any website or online service that collects or processes personal data of individuals residing in the EU, regardless of where the website itself is hosted. This means if you have even a single EU member in your phpFox community, GDPR applies to you.
The core of GDPR revolves around empowering individuals with more control over their personal data. It outlines several key principles, including:
- Lawfulness, Fairness, and Transparency: You must have a legitimate reason for collecting data, be transparent about what you collect, and use it fairly.
- Purpose Limitation: Data should only be collected for specified, explicit, and legitimate purposes and not further processed in a manner that is incompatible with those purposes.
- Data Minimization: Only collect data that is necessary for your stated purpose.
- Accuracy: Keep personal data accurate and up to date.
- Storage Limitation: Retain data only for as long as necessary.
- Integrity and Confidentiality: Protect personal data from unauthorized or unlawful processing and from accidental loss, destruction, or damage.
- Accountability: You, as the data controller, are responsible for demonstrating compliance with GDPR.
Key GDPR Considerations for phpFox Community Owners
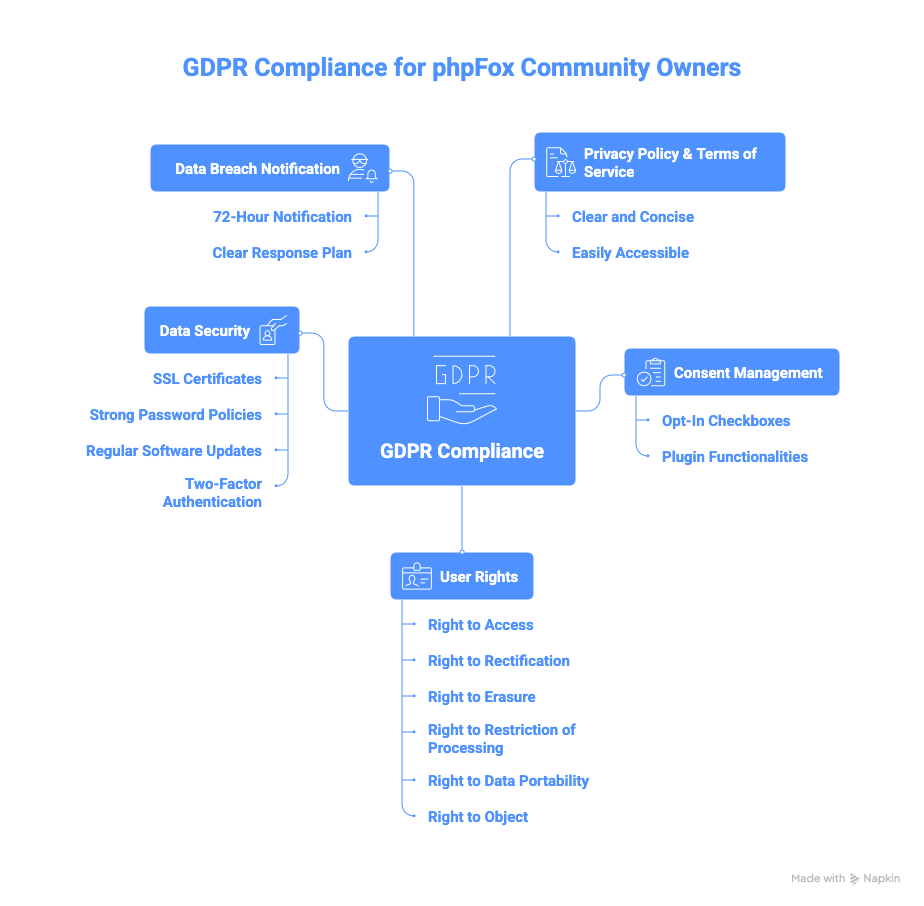
- Privacy Policy & Terms of Service: This is your foundational document. Your privacy policy must be clear, concise, and easily accessible, detailing what data you collect, why you collect it, how you use it, who you share it with, and how users can exercise their rights. Your terms of service should outline user responsibilities and platform policies related to data. Make sure these are up-to-date and reflect your current data practices.
- Consent Management: GDPR places a strong emphasis on explicit consent. For certain types of data processing, particularly for non-essential cookies or marketing communications, you need to obtain clear, affirmative consent from your users. This often involves opt-in checkboxes rather than pre-checked boxes. phpFox offers various plugins and functionalities that can help manage consent for cookies and other data collection points.
- User Rights: GDPR grants individuals several key rights regarding their data:
- Right to Access: Users can request to see what personal data you hold about them.
- Right to Rectification: Users can request corrections to inaccurate data.
- Right to Erasure (“Right to be Forgotten”): Users can request the deletion of their personal data under certain circumstances.
- Right to Restriction of Processing: Users can request that you limit the way you use their data.
- Right to Data Portability: Users can request to receive their data in a structured, commonly used, and machine-readable format.
- Right to Object: Users can object to certain types of data processing.
You need to have mechanisms in place within your phpFox community to facilitate these requests efficiently.
- Data Security: Protecting user data from breaches is crucial. This involves implementing robust security measures, such as SSL certificates, strong password policies, regular software updates for your phpFox instance and server, and potentially two-factor authentication. Regularly review your security practices and educate your team and users on best practices.
Data Breach Notification: In the event of a data breach, GDPR requires you to notify the relevant supervisory authority within 72 hours of becoming aware of it, and in some cases, notify the affected individuals without undue delay. Having a clear data breach response plan is essential.
Practical Steps for phpFox Owners
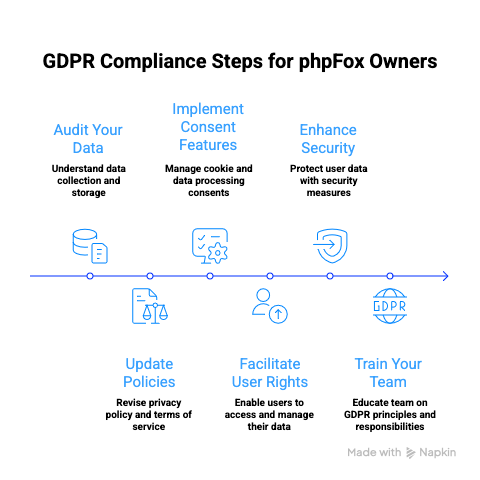
- Audit Your Data: Understand what personal data your phpFox community collects, where it’s stored, and why you collect it.
- Update Policies: Review and update your privacy policy and terms of service to be GDPR compliant.
- Implement Consent Features: Utilize phpFox’s capabilities or add-ons to manage cookie consent and other data processing consents.
- Facilitate User Rights: Ensure users can easily access, rectify, delete, or port their data. Consider creating a dedicated section in user profiles or through a support ticket system.
- Enhance Security: Implement all necessary security measures to protect user data.
- Train Your Team: Ensure anyone with access to user data understands GDPR principles and their responsibilities.
Navigating GDPR can seem daunting, but it’s an opportunity to build a more transparent and trustworthy community. By proactively addressing these compliance requirements, you not only protect your platform from legal repercussions but also foster a stronger, more respected environment for your phpFox members.
Ready to build a community that is secure, transparent, and trustworthy?
phpFox provides a robust platform with tools designed to help you manage user data and meet complex compliance requirements like GDPR. We handle the technical challenges, so you can focus on what matters most: connecting and growing your community.
Start your 14-day free trial of phpFox today!